Security Is Our Foundation
Enterprise-grade security infrastructure built for Wall Street's most demanding requirements. Every layer of our platform is engineered to protect your most sensitive financial data.
Independently Verified Security
Our security posture is validated by the industry's most rigorous independent audits.
SOC 2 Type II
Independently audited controls for security, availability, processing integrity, confidentiality, and privacy. Our SOC 2 Type II report demonstrates sustained compliance over time, not just a point-in-time snapshot.
SOC 1
Independently audited internal controls over financial reporting. Our SOC 1 report provides assurance that Loffa's settlement and compliance processes meet the standards required by our clients' financial auditors.
Multi-Layer Security Architecture
Our platform employs a defense-in-depth strategy with multiple overlapping security layers. Each ring of protection operates independently, ensuring that no single point of failure can compromise your data.
- Perimeter Security — Web application firewalls, DDoS protection, and intrusion detection
- Network Security — Encrypted tunnels, network segmentation, and micro-segmentation
- Application Security — Secure SDLC, code review, and penetration testing
- Data Security — AES-256 encryption at rest, TLS 1.3 in transit, tokenization
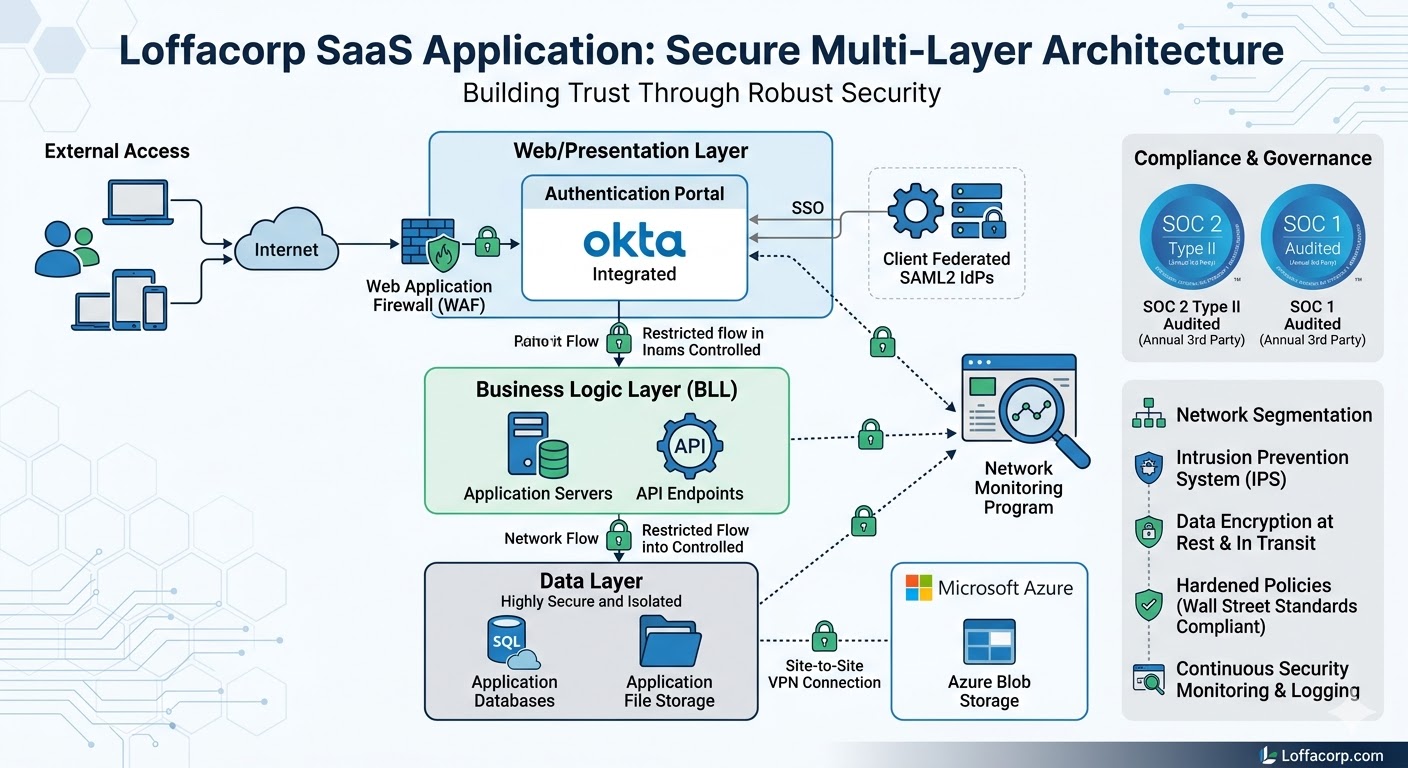
Enterprise-Grade Data Centers
Your data runs in professionally operated data centers and cloud infrastructure from independently audited providers.
Secure Data Centers
Production runs in professionally operated data centers with controlled physical access, 24/7 on-site security, and redundant power and cooling.
Audited Providers
Every hosting provider we use is independently audited, and we review each one every year as part of our vendor management program.
Backup & Recovery
Encrypted backups and a separate recovery environment protect against the loss of a site. Our recovery procedures are documented and covered by our SOC 2 Type II audit.
24/7 Surveillance
Round-the-clock security monitoring with real-time alerting and a documented response process.
99.99% Uptime SLA
Guaranteed availability backed by redundant power, networking, and compute resources.
Details Under NDA
Our SOC reports, policies, architecture, recovery targets, and provider list are available to clients and prospects under NDA. Request the security package.
Comprehensive Security Controls
Rigorous policies and technical controls ensure your data is protected at every level of our operations.
Access Management
Role-based access control (RBAC) with least-privilege principles. Multi-factor authentication, SSO integration, and comprehensive audit trails for every access event.
Encryption
AES-256 encryption for data at rest and TLS 1.3 for data in transit.
Continuous Monitoring
Centralized security logging and alerting, with continuous vulnerability scanning.
Incident Response
Documented incident response plan with defined escalation paths and communication protocols. Regular tabletop exercises and post-incident reviews ensure continuous improvement.
Vendor Management
Rigorous third-party risk assessment program with ongoing monitoring of vendor security postures. All sub-processors undergo annual security reviews and contractual obligations.
Regulatory Compliance
Purpose-built for SEC, FINRA, and DTCC regulatory requirements. Automated compliance workflows ensure adherence to evolving financial industry regulations.
Ready to See Our Security in Action?
Schedule a security briefing with our team. We'll walk you through our architecture, audit reports, and how we protect the world's largest financial institutions.